
The recent Coldcard exploit, which has drained over 1,300 Bitcoin (BTC) valued at approximately $83 million, has ignited a sharp debate within the cryptocurrency community. Bitcoin security researcher and Casa co-founder Jameson Lopp argues the incident starkly exposes the practical limitations of the network’s foundational “don’t trust, verify” mantra.
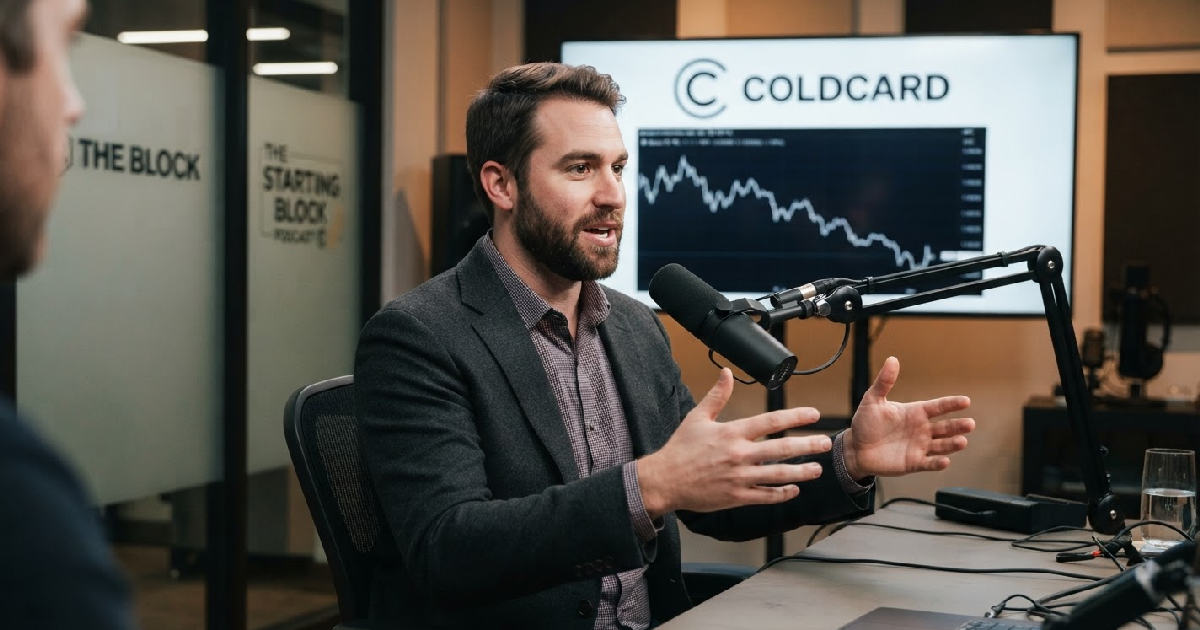
While the exploit became publicly known recently, with core thefts occurring on Thursday, July 30, 2026, Lopp’s pointed comments were made on Monday, August 3, 2026, during The Block’s The Starting Block podcast.
Understanding the Coldcard exploit’s architecture
This multi-million dollar theft challenges the long-held notion that most users can truly verify the complex hardware and software underpinning their self-custody solutions. It forces a reckoning with where trust inevitably settles, even in systems explicitly designed to minimize it. For Lopp, it’s a critical moment for the industry to realistically assess the nature of trust in a decentralized world.
The Coldcard exploit stems from a critical flaw introduced in March 2021 within the hardware wallet’s seed-generation process. A build-configuration error occurred during a migration of elliptic-curve operations to Bitcoin Core’s libsecp256k1 library.
This error caused a macro named MICROPY_HW_ENABLE_RNG to be inadvertently defined as zero. Unfortunately, the supporting libngu library only checked for the macro’s definition, not whether it was actually enabled, bypassing the intended true hardware random number generator (RNG).
Consequently, Coldcard devices defaulted to a weaker MicroPython software fallback for randomness during seed creation. Instead of the anticipated 128 bits of entropy promised for secure 12-word BIP-39 seeds, affected devices produced seeds with significantly less, rendering them predictable and vulnerable to brute-force attacks.
This vulnerability directly impacted Coldcard Mk3 and later models running firmware versions 4.0.1 through 5.0.3. Seeds generated on Mk2 or Mk3 devices using firmware from 4.0.1 up to and including 4.1.9 were particularly susceptible, and the exploit didn’t even require physical access to the wallets.
Automated theft and multi-wave attacks
Attackers leveraged this critical flaw to execute a highly automated and coordinated assault on vulnerable wallets. The initial wave of thefts unfolded rapidly on Thursday, July 30, 2026, between 01:31 and 01:56 UTC.
During this swift 25-minute window, 594.48 BTC, valued at approximately $38 million at the time, was stolen from about 500 Bitcoin addresses. These funds were efficiently consolidated into a single address holding 562 BTC, demonstrating the attack’s precision.
Blockchain researchers, including Galaxy Digital head of research Alex Thorn, have since identified multiple subsequent waves of thefts. By Sunday, August 2, 2026, Thorn noted a potential fourth wave, indicating ongoing exploitation of the vulnerability.
Broader analysis connected roughly 1,196 addresses to the exploit, with as much as 1,083 BTC, valued at nearly $70 million, drained over a period of approximately 41 minutes. The speed of these operations, characterized by elevated fixed transaction fees and no change outputs, strongly suggested the use of prepared lists of private keys.
Lopp’s call for realistic trust assessment
Jameson Lopp, a vocal proponent of self-custody, acknowledges the inherent value of “don’t trust, verify.” Yet, he argues the Coldcard exploit reveals a fundamental practical barrier. “It’s a good mantra … But you have to understand that verification of complex software and hardware is simply not feasible for 99.9% of the population,” Lopp stated.
His point isn’t to dismiss the principle itself, but to highlight the reality that most users don’t have the technical expertise or resources to audit complex cryptographic systems. This leaves them in a precarious position, forced to rely on external assurances.
“Ultimately, what happens is … we end up trusting someone that we suspect has verified it,” Lopp explained. This sentiment underscores a critical paradox in decentralized systems: while they aim to remove intermediaries, the complexity of implementation often reintroduces layers of trust in specialists.
Zach Herbert, co-founder and CEO of Foundation, echoed this view, emphasizing that the incident shouldn’t invalidate self-custody. Instead, Herbert suggested, it should serve as a catalyst for the industry to strengthen best security practices and improve user education around the responsibilities involved.
The Coinkite customer record conundrum
Adding another layer to the trust discussion is Coinkite’s policy regarding customer data. Lopp highlighted what he termed a “fun double-edged sword” concerning the hardware wallet manufacturer’s practice of purging customer records.
“Coinkite purges all their customer records after 120 days to protect against data breaches,” Lopp noted. While this policy aims to enhance privacy, it also meant the company was unable to proactively warn customers who had purchased vulnerable Coldcard devices over the past five years.
This situation presents a difficult trade-off between privacy protection and critical security communication. It forces a question about the optimal balance for hardware wallet manufacturers in managing user data and incident response, pushing trust onto firms to self-report issues to a community they cannot directly contact.
AI’s accelerating role in vulnerability discovery
Another significant dimension to the Coldcard exploit, according to Lopp, is the likely role of artificial intelligence in its discovery. He believes advancements in large language models (LLMs) are dramatically altering the security landscape, enabling attackers to uncover obscure software flaws more rapidly than ever before.
“Advancements in large language models are drastically changing the security landscape,” Lopp asserted, pointing to a growing trend of AI unearthing vulnerabilities in widely used products. This creates an intense, accelerating race between those seeking to exploit weaknesses and those striving to defend against them.
While AI empowers attackers to identify flaws, it also significantly reduces the cost of code review for defenders. This dynamic means both sides are leveraging advanced computational tools, leading to a faster, more volatile security environment where vulnerabilities can emerge and be exploited with unprecedented speed.
Coinkite CEO Rodolfo Novak, who publicly took responsibility for the firmware bug, similarly framed the incident as “a sober reality of the new AI paradigm.” Novak underscored how AI-assisted code review could uncover latent vulnerabilities quicker than even experienced human security researchers, potentially giving attackers an edge in exploiting publicly available code.
Despite the substantial losses from the Coldcard exploit, Lopp maintains that the fundamental value proposition of self-custody remains unchanged. He emphasizes that the incident primarily reinforces the significant responsibilities that users must embrace when choosing to secure their own digital assets.
“Self-custody is for anyone willing to take on the responsibility that comes with it,” Lopp said, pushing back against any notion that the exploit invalidates the practice itself. He views such incidents as unfortunate but inevitable lessons in a continuously evolving security environment.
Critical hardware wallet failures aren’t unprecedented, and each historically leads to an industry-wide reevaluation and ultimately higher security standards. The core challenge for the Bitcoin community now is to openly recognize these inherent assumptions of trust and actively work to reduce them wherever technically feasible, empowering individuals with genuine verification tools rather than blind faith.