
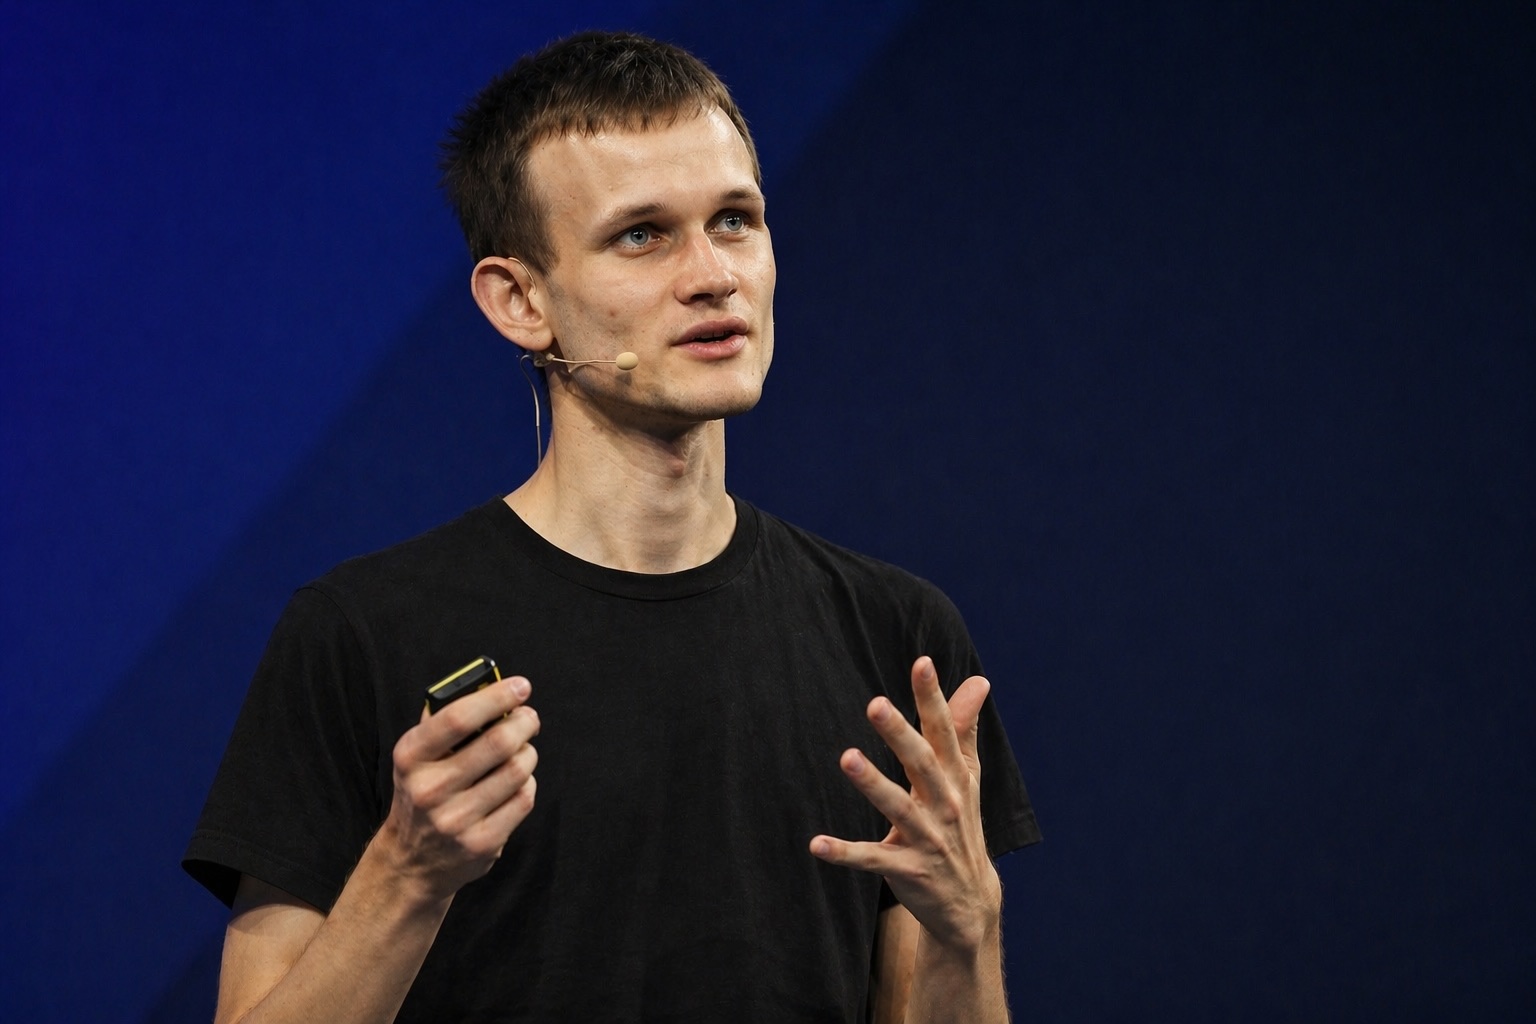

Ethereum co-founder Vitalik Buterin is pushing back on one of the internet’s more anxious ideas: that AI will eventually make crypto security impossible to defend.
In a Wednesday post on X, Buterin argued that increasingly capable AI could actually strengthen crypto security, helping developers mathematically verify even highly complex software. The technology that can uncover vulnerabilities, in his view, could also become one of the best tools for finding and fixing them.
That matters because the stakes are unusually high in crypto. Buterin said that roughly 90% of his own net worth is in crypto, making the question of whether security can keep up with AI more than an abstract exercise.
“It’s an increasingly common take that AI hacking means cybersecurity is doomed,” Buterin wrote. “I disagree. I think cybersecurity is naturally defense-favoring once people get their shit together.”
His argument centers on formal verification, a method that uses mathematical proofs to establish whether software satisfies specific security requirements.
Buterin sees AI as potentially pushing that process far beyond the limited pieces of code developers typically examine today. “If AI can prove Navier-Stokes and FLT, then AI can prove the statement ‘this program is secure’ as a mathematical theorem,” he wrote. “Even if the program is very complicated.”
Crypto security has a new trick up its sleeve
There is an important catch. Proving that software is secure is only useful once developers have clearly defined what “secure” is supposed to mean. Buterin identified that problem as the difficult part.
Still, developers are already putting AI to work on the defensive side of crypto security. AI agents are being used to scan code, probe for exploits, and identify bugs before attackers can exploit them.
The pressure has intensified after several incidents raised concerns that AI could be giving hackers a significant advantage.
In May, security researcher Taylor Hornby used Anthropic’s Claude Opus 4.8 to find a four-year-old vulnerability in Zcash’s Orchard privacy pool. The flaw could have allowed unlimited, undetectable counterfeiting of ZEC. Developers found no evidence that it had been exploited and patched it in June.
Ethereum researchers reported another warning sign in July, when Foundation researchers said AI agents had uncovered vulnerabilities in critical network infrastructure.
That same month, attackers began draining Coldcard wallets through an old firmware flaw that weakened seed generation, resulting in roughly $130 million worth of stolen Bitcoin. Coinkite, the company behind Coldcard, said AI likely helped attackers identify the vulnerability.
By August, the concern had moved deeper into Bitcoin’s software ecosystem. Boltz suspended its swap service after saying suspected attackers were discovering flaws faster than its developers could repair them. Core Lightning also confirmed that several vulnerabilities identified in AI-generated reports were real.
The response has become increasingly machine-assisted on the other side, too. The volunteer Bitcoin Red Team used AI-assisted audits to identify 4,962 potential vulnerabilities across 390 projects.
Buterin’s larger point is that this contest does not necessarily have to end with attackers winning. He said AI can now move toward verifying entire programs rather than isolated components, an approach Ethereum intends to pursue over the next several years.
“There is no future for blockchains—especially blockchains with scalability and privacy—without doing this,” he said. “We need to make software actually secure. And we have already made a lot of progress.”
The debate around AI and hacking often treats defense as a race to survive whatever attackers invent next. Buterin is proposing a different possibility: use increasingly capable AI not just to find holes, but to mathematically demonstrate that certain classes of software behave as intended.
For crypto security, that would mean shifting part of the battle from reacting to exploits toward proving that vulnerabilities should not exist in the first place.